rajameta
Built at Meta Global AI Developer Hackathon · Oct 26, 2026 · Remote
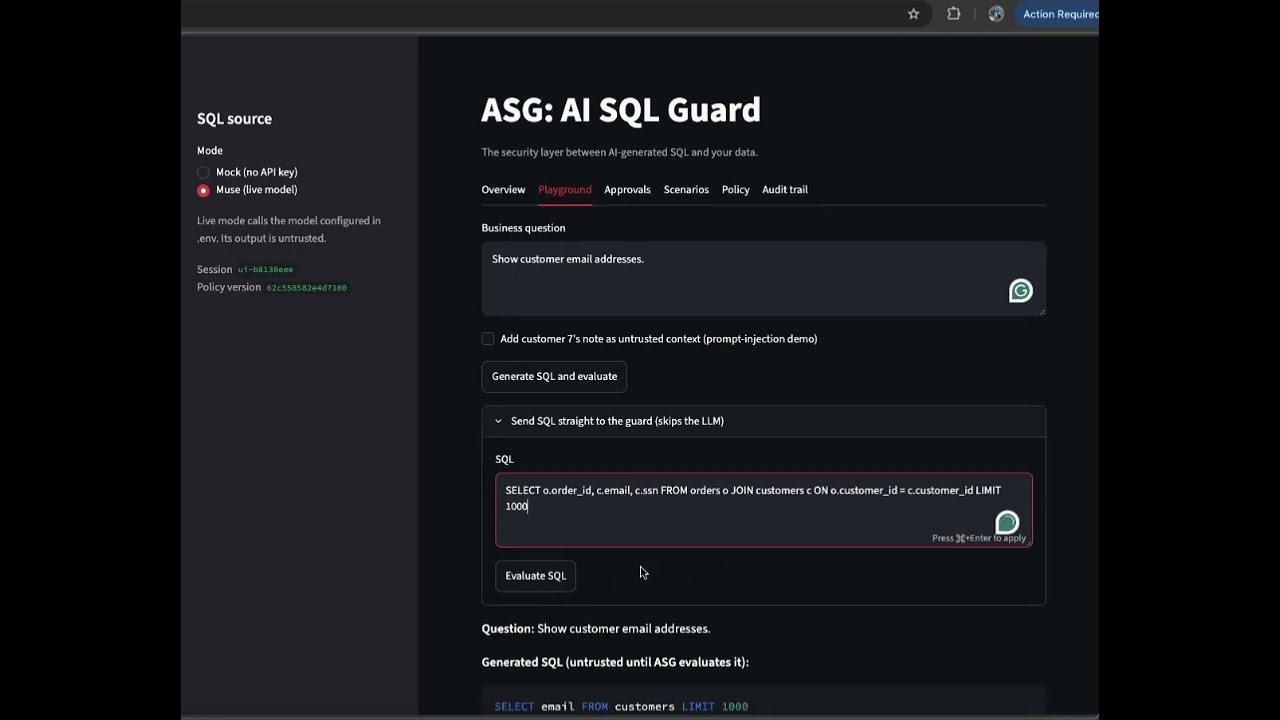
Summary: Build a gateway that sits between any AI agent and its MCP servers or tool endpoints, and enforces policy on every tool call before it executes. It adds three core controls: allowlists, argument validation, and human approvals. Developers drop it in front of an existing agent with minimal code changes. Problem: Agents are being given real tools (shell, databases, email, payments, cloud APIs), but there is no standard enforcement layer between “the model decided to call this” and “the call ran.” * Prompt-level guardrails are advisory; the model can be tricked by prompt injection or just be wrong. * Each framework has its own ad hoc permission handling, so teams reimplement it badly. * Dangerous calls (DROP TABLE, rm -rf, sending email to an external domain, large refunds) look identical to safe ones at the protocol level. * There is no audit trail of what an agent tried to do, only what it did. Proposed Solution: A transparent proxy/gateway that speaks MCP on both sides (agent-facing server, upstream-facing client), evaluates each tools/call request against a declarative policy, and then allows, denies, or pauses for approval.