Skip to Main Content

Clawdit auto-discovers your OpenClaw agent's linked Google account and makes it send malicious emails and calendar invites to itself. If the agent follows hidden instructions when processing them, you have a vulnerability. It also runs baseline checks for prompt injection, data leakage, unauthorized actions, and access control. Attack variants are generated and evaluated by Llama 3.3 70B on Nebius Token Factory, with Tavily providing real-time threat intelligence to keep attacks current. Fully self-contained -- no extra credentials, no third parties. The agent attacks itself; Clawdit just watches and scores.

Team

jww

More from Nebius.Build SF

Injester is an AI-native engine that transforms "agent-hostile" websites into structured data interfaces. While the web was built for human attention, our…

Injester project preview

Generating the first human preference datasets for robot policies in simulation with Nebius GPUs to understand which policies work best in an objective way…

Chase Brignac project preview

RoboStore is a self-expanding robot agent platform that enables robots to autonomously detect their own capability gaps, search for hardware solutions in…

RoboStore project preview

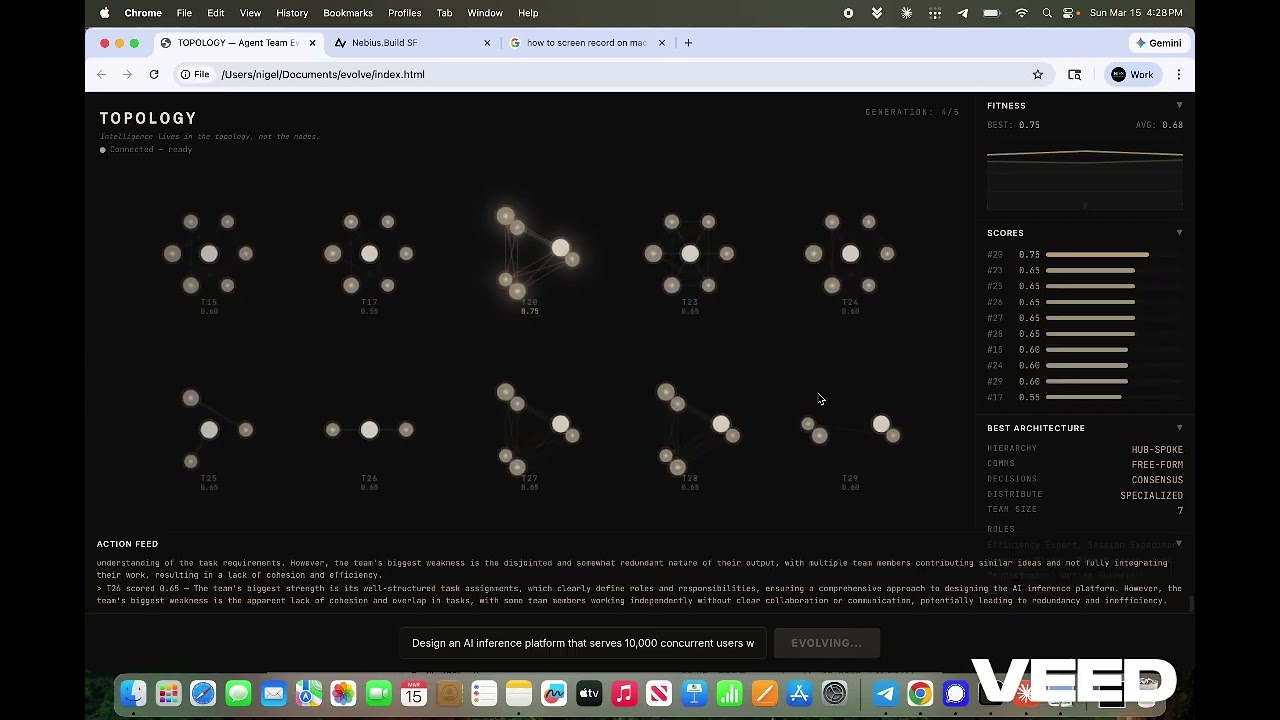
10 teams of LLM agents compete on a task. Each team has a randomly generated organizational genome — hierarchy, communication pattern, decision-making style…

Topology project preview

Asha is a WhatsApp-native AI assistant that helps small home-based food businesses manage orders and remember customers — all through WhatsApp, with no apps…

Asha project preview

robots that undestand the surroundings. location and mapping

jimmy project preview