24H
Built at Meta Global AI Developer Hackathon · Oct 26, 2026 · Remote
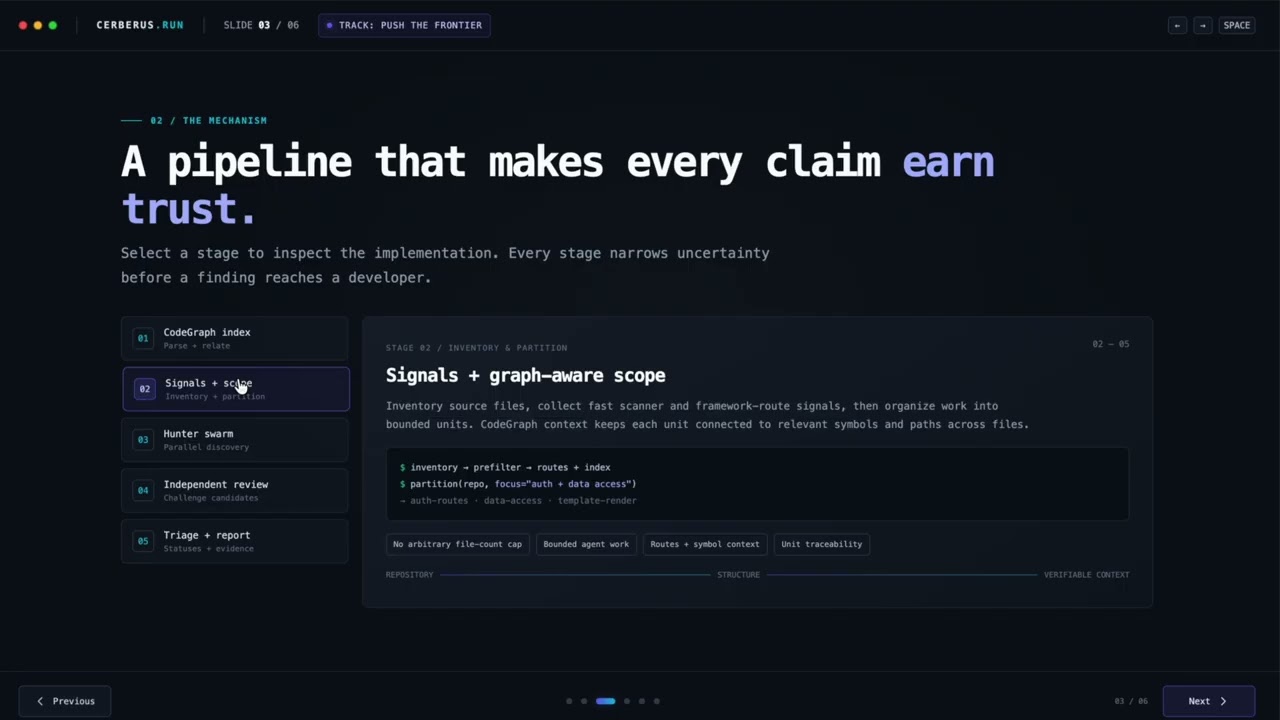
Static application security testing (SAST) tools routinely miss contextual business-logic flaws, while naive LLM scanners flood engineering teams with high-confidence hallucinations. A model can hypothesize a flaw, but without structural context or runtime verification, it cannot tell if a vulnerability is reachable or mitigated by upstream controls. Cerberus pushes the frontier of autonomous software capabilities by turning Meta’s models into a mechanically grounded vulnerability hunting and verification engine. Rather than accepting model outputs as final verdicts, Cerberus treats them as untrusted hypotheses that must survive multi-stage static and dynamic validation: AST CodeGraph Intelligence & Pre-filtering: Cerberus parses source trees across 13+ languages using Tree-sitter grammar helpers and indexes them into a relational SQLite .codegraph capturing symbol definitions, calls, and references edges. It pairs this with ~40 stack-aware pattern groups (tools/sast.py) to gather contextual signals across injection sinks, SSRF, deserialization, and authentication boundaries. Deterministic Module Partitioning: An indexed partitioner breaks large repositories into focused hunter units by analyzing module structures, directory proximity, graph links, and size budgets—giving models deep, bounded context without token-window exhaustion. Hunter & Validator Swarms: Specialized hunter agents inspect code units to identify attack vectors. Findings are routed into validation cells where independent validator agents cast discrete status votes (confirmed, fp, needs-review). Findings require a strict majority (1–5 configurable votes) to escalate; ties default to needs-review. Dual-Control Sandboxed Verification: High-severity findings can be dynamically verified inside a resource-capped execution runtime (local read-only FS or Docker containers capped at 2 CPUs and 2 GB RAM). A model-synthesized reproduction script is certified as proven only when all reproduction runs exit 0 with a line-anchored [POC_PROVEN] sentinel and a control run exits 0 with [POC_CONTROL_PASSED]. Standardized CI/CD Integration: Audits produce actionable artifacts including SARIF, interactive HTML dashboards, JUnit, and structured JSON logs. In active benchmark testing across real-world open-source repositories, Cerberus demonstrates 75.3% macro recall, 72.6% macro precision, and 73.4% macro F1 across 280 validated true positives.