Soojal Labs
Built at Meta Global AI Developer Hackathon · Oct 26, 2026 · Remote
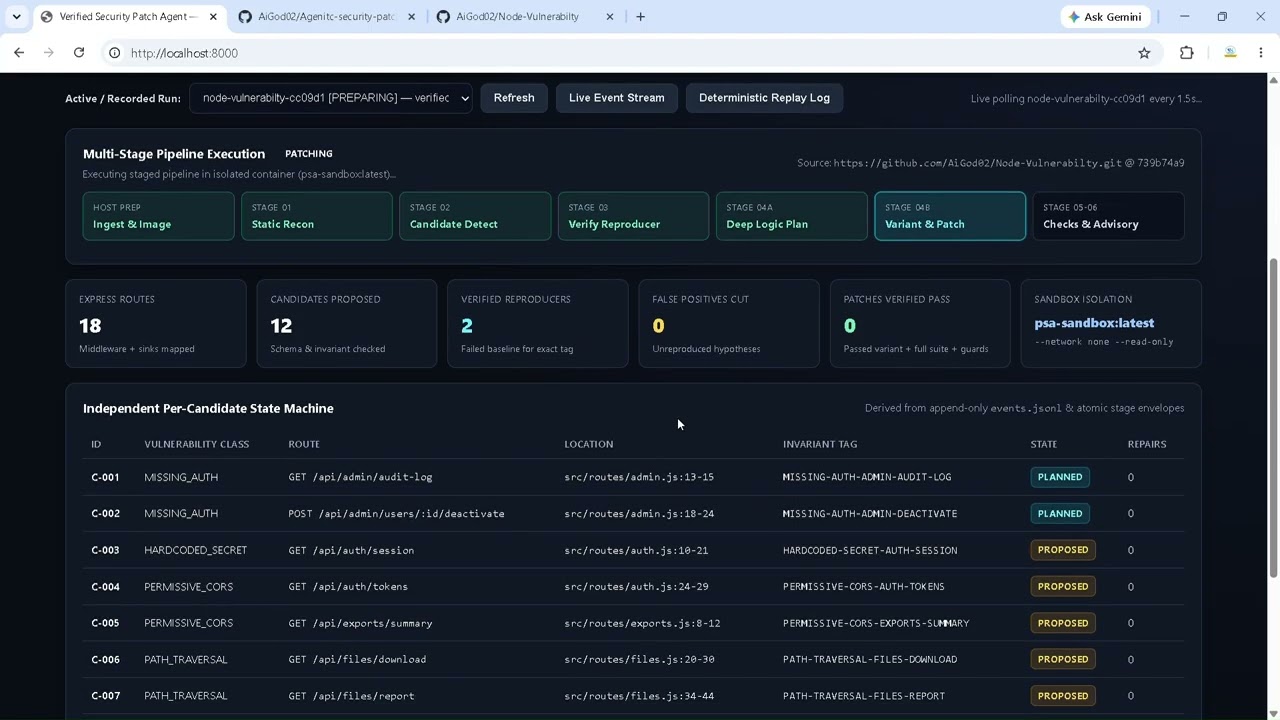
Verified Security Patch Agent is an AI agent that finds and fixes security vulnerabilities in Node.js/Express repositories, and proves every finding and every fix with real execution, not model guesswork. The problem: AI coding agents often write security patches by guessing. They introduce regressions, hallucinate APIs, or “pass” tests by deleting the vulnerable route entirely. Developers can’t trust the output. How it works: Paste any Express repo URL, and a 7-stage pipeline runs: Static recon maps routes, middleware, auth checks and parameter sinks. Candidate generation: Meta’s Muse Spark proposes vulnerability hypotheses across six OWASP classes (IDOR, SQL/command injection, path traversal, missing auth, hardcoded secrets, permissive CORS). Sandboxed reproduction: each finding must be reproduced in a hardened Docker sandbox (no network, read-only root, dropped capabilities) with a test that fails deterministically twice. A companion test proves legitimate usage still works. Anything that doesn’t fail reliably is discarded as a false positive. Planning and patching: Meta’s Muse Wonder plans a minimal fix with verified file-and-line evidence, and writes a held-out variant test the patch model never sees, so the fix can’t overfit to the original test. Mechanical guards cap diffs at 40 lines, keep test directories byte-identical, and block removed routes. Evidence advisory: a 9-section report where every cited line and snippet is checked against the real files. Human approval: approval is bound to the SHA-256 hash of the exact diff, so changing even one character voids it. The fix is committed to an isolated review branch, and nothing is ever auto-merged. Why it matters: Developers get security fixes they can verify rather than trust, with a clear audit trail and humans in control. It works on real repositories today. Built solo with Python, FastAPI, LangGraph, Docker, and the Meta Model API (Muse Spark, Muse Wonder). Links: Agent repo: github.com/AiGod02/Agenitc-security-patch Demo target: github.com/AiGod02/Node-Vulnerabilty