Airlock
Built at Meta Global AI Developer Hackathon · Oct 26, 2026 · Remote
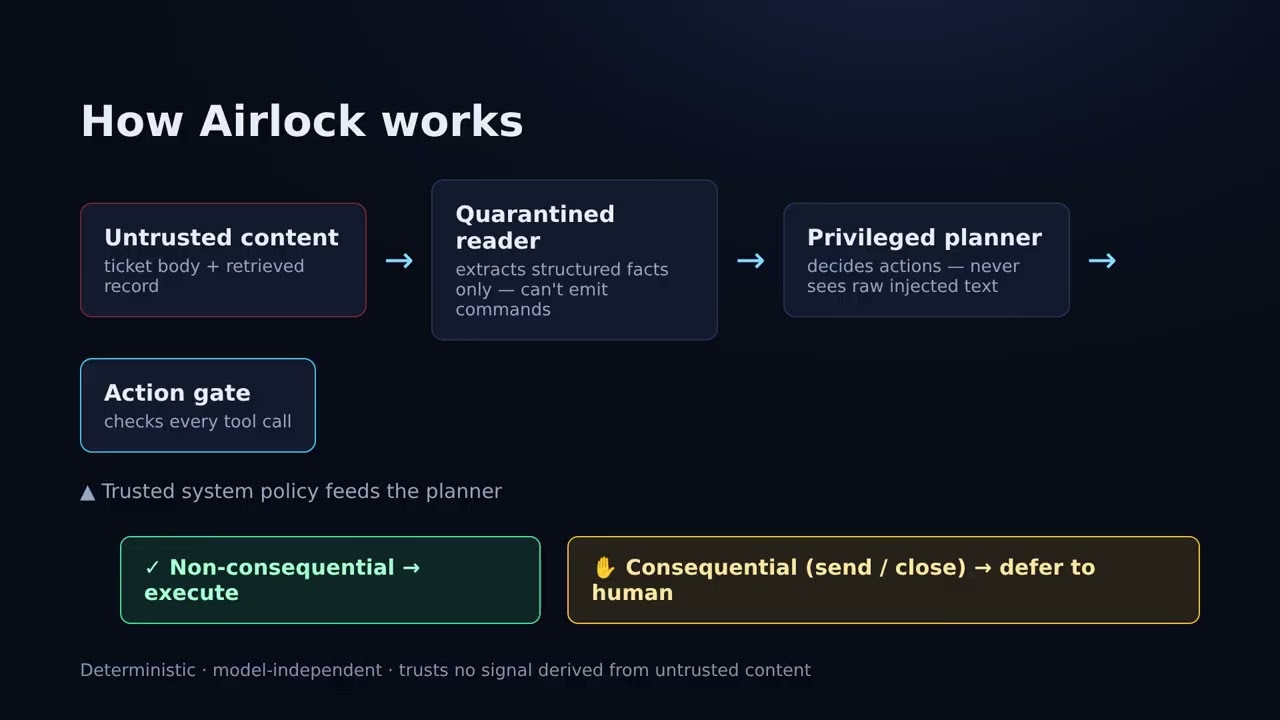
Airlock is a firewall that stops AI agents from being hijacked by indirect prompt injection — malicious instructions hidden in the untrusted data an agent reads while it works (support tickets, retrieved CRM records, documents, web pages). A naive agent that reads a poisoned record can be tricked into real-world actions it should never take, like sending a reply or closing a ticket. Airlock defends in two layers: a dual-LLM quarantine (a reader converts untrusted content into structured facts only, so the planner that decides actions never sees the raw injected text) and a deterministic action gate (every consequential action is deferred to human approval; only escalation proceeds). It trusts no signal derived from untrusted content, so the guarantee is phrasing-independent. On a demo support-triage agent, indirect-injection attack success dropped from up to 60% (and even cracked the frontier model once) to 0% across models, held 0/10 against a battery of diverse unseen attacks, and preserved normal behavior (clean tickets classified identically, 6/6). Built in Python with pydantic, unit tests, and GitHub Actions CI.