Skip to Main Content

ShipSec Local is a local-first security review plugin and workflow for Codex. It builds a repo-wide security model, saves a trusted baseline, and then compares the current working state against that baseline to surface newly introduced attack vectors, widened trust boundaries, and important existing risks. It also supports clean-room verification in Docker so teams can run the same review flow in an isolated Codex environment.

Team
betterclever

More from The IDE Reimagined: JetBrains Codex Hackathon

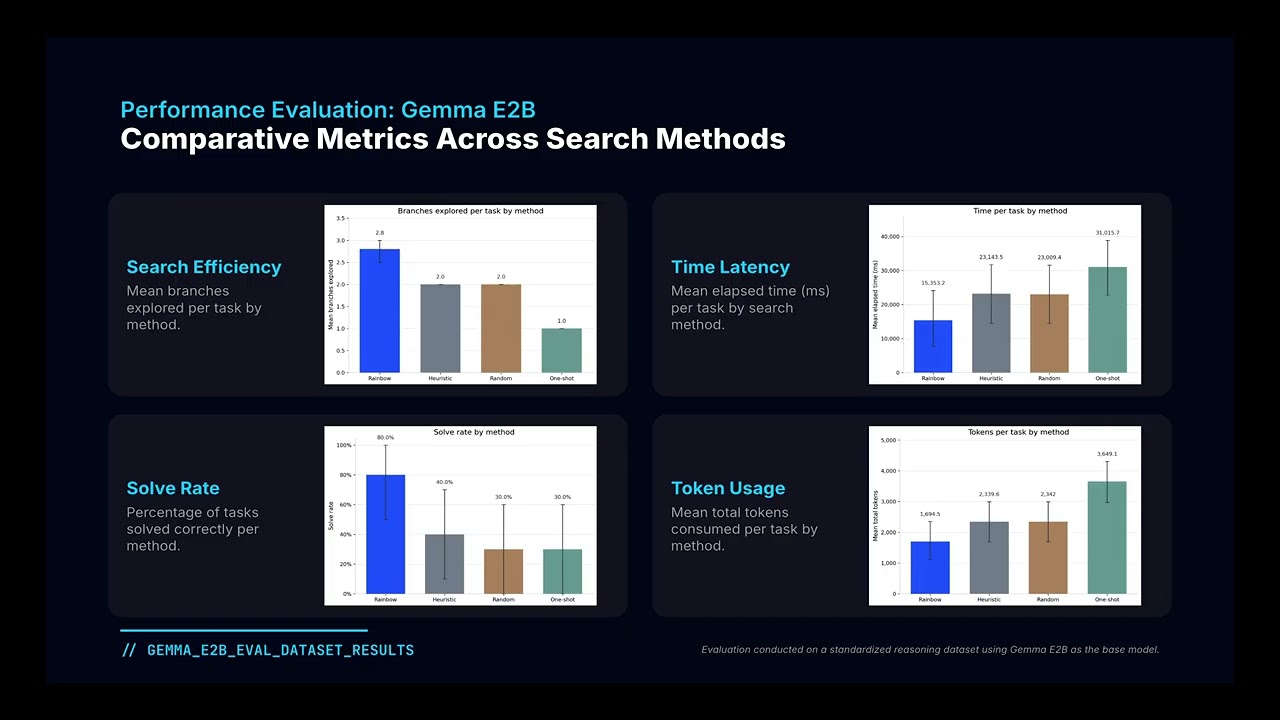
We built a self-healing coding agent that searches over compact DSL implementation plans before generating code. The LLM proposes semantic reasoning branches…

thinking project preview

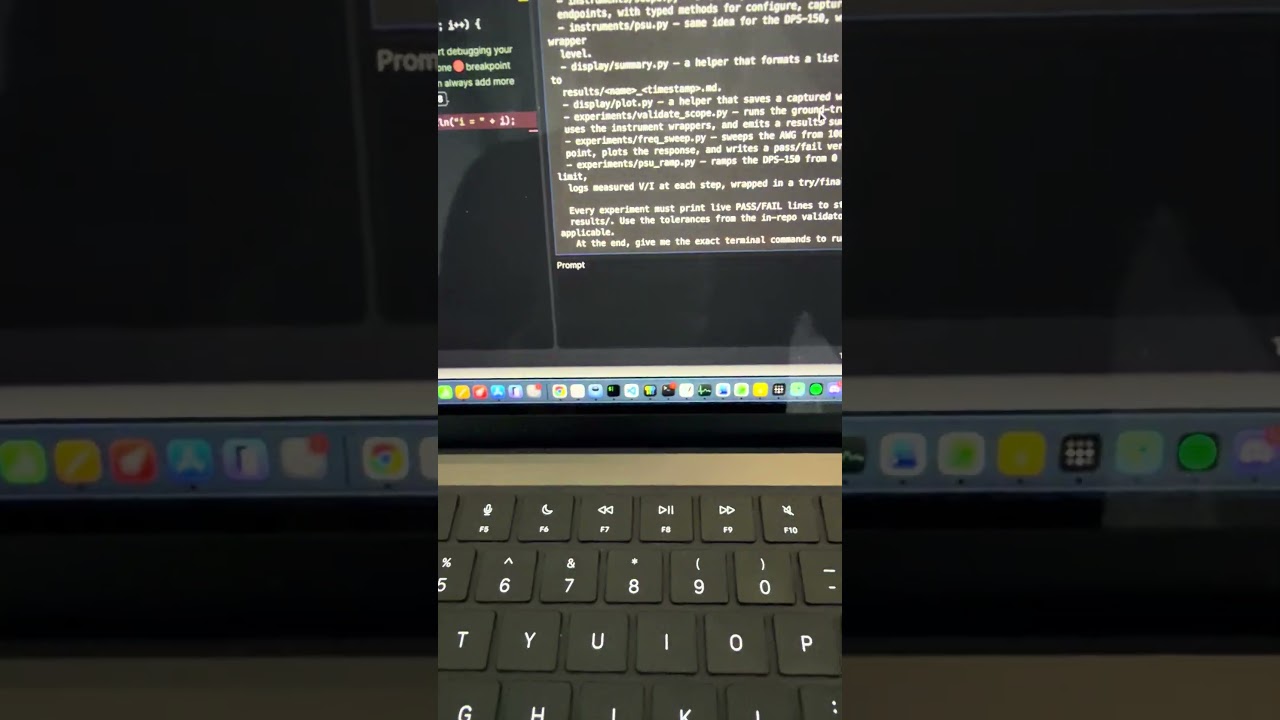
Scopecreep turns your JetBrains IDE into an agentic hardware testbench. Describe a test in plain English; an AI agent writes Python directly into your open…

Scopecreep project preview

Mesh Code: shared session state for coding agents. Install mesh-code-mcp in any IDE and any agent — Claude, Cursor, Codex — sees the same feature card, event…

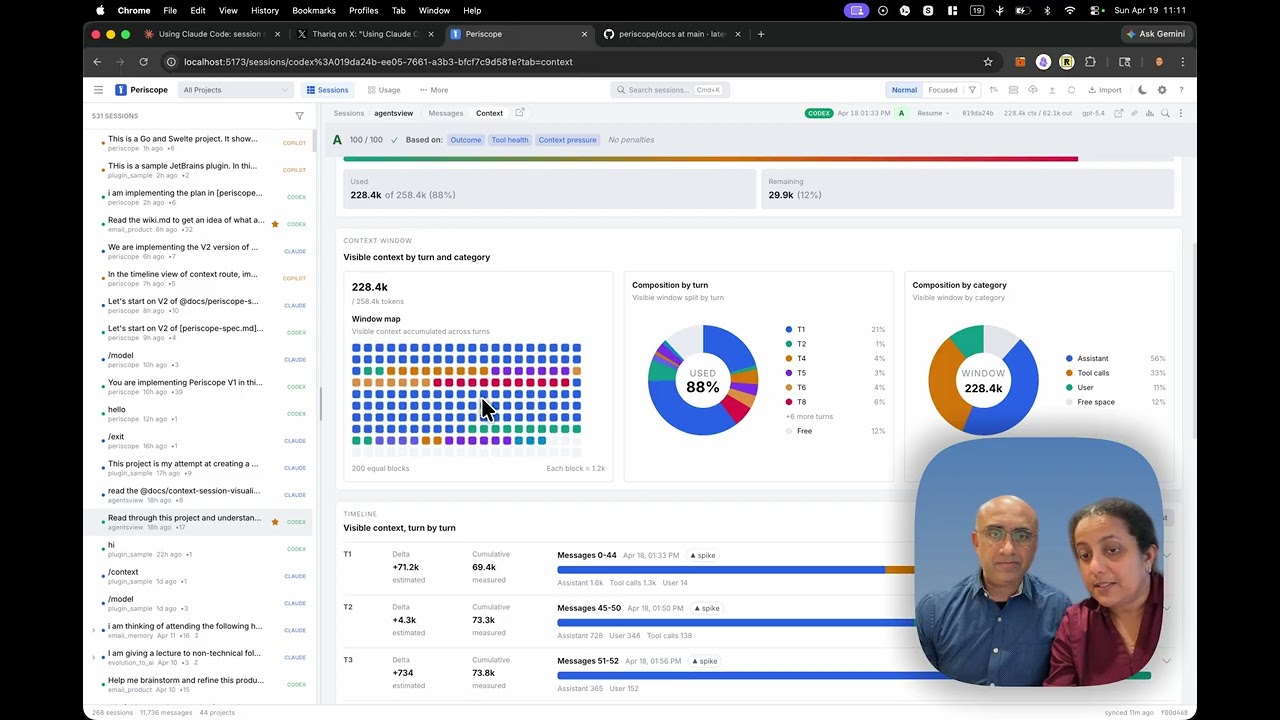
Periscope is a local-first viewer that shows you exactly what's in your coding agent's context window, turn by turn, and tells you what to do about it. What…

Latent Signal project preview

SecureLoop turns production Sentry alerts into Codex-generated, sandbox-tested, human-approved fixes inside JetBrains.

SecureLoop project preview

Pinpoint is a visual annotation overlay for frontend review. Not just that, it also helps pinpoint things in complex software :)