JATAYU
Built at Gemini 4 Argon SF Hackathon · Oct 25, 2026 · San Francisco, CA
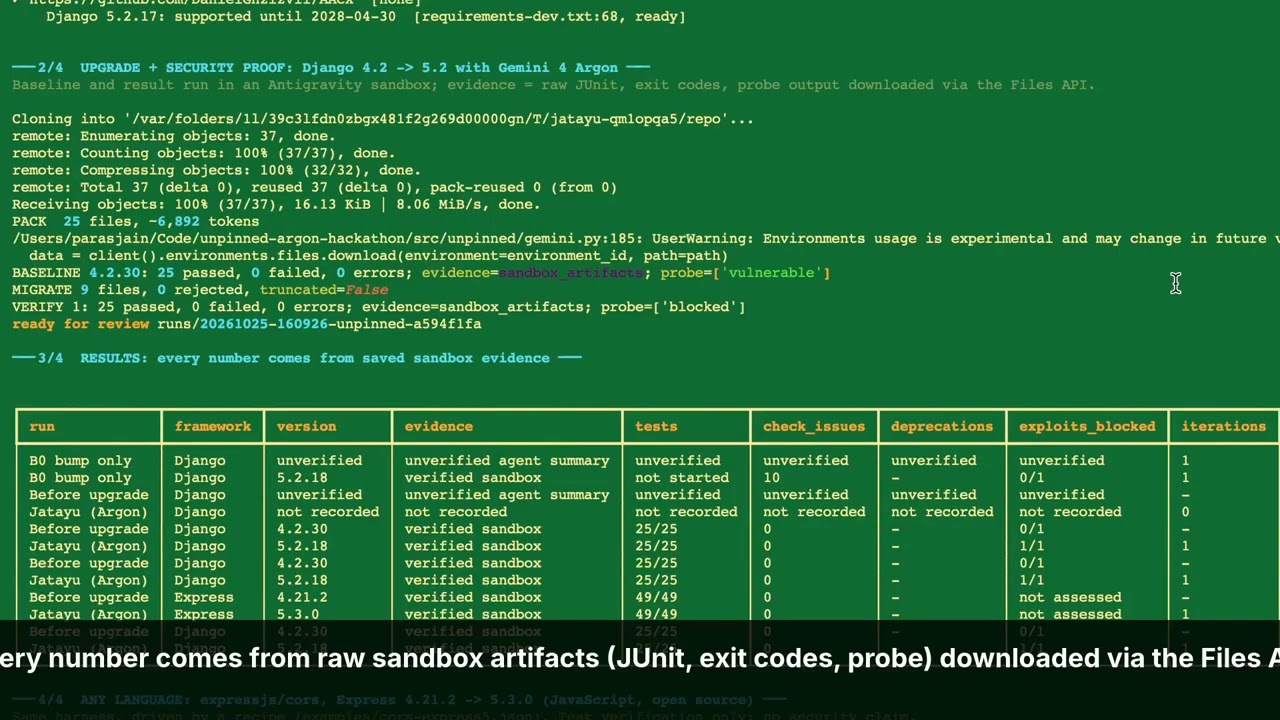
Jatayu takes on the security upgrade that every team puts off. When a framework reaches end of life, it stops getting security fixes. The fix is a major-version upgrade that touches every file, so it sits in the backlog while the app stays exposed. Fleet scans repositories and flags every app on an unsupported framework or runtime, with file:line evidence from endoflife.date data. For each app it picks, Jatayu: runs the baseline tests and a security exploit in an Antigravity sandbox; has Gemini 4 Argon rewrite every affected file in one long-decode response; re-runs the tests and the exploit in a fresh sandbox. Every result comes from raw sandbox artifacts (JUnit, exit codes, probe output) downloaded through the Files API, never from the model’s own summary. Jatayu also rejects patches that weaken tests and checks that its harness files come back byte-for-byte. Nothing reaches GitHub until a human approves the exact patch, bound by its SHA-256. Results from today’s runs: Django 4.2 → 5.2: 25/25 tests passed before and after. The CVE-2026-87975 exploit went from succeeding to blocked. Language-agnostic (expressjs/cors), Express 4.21.2 → 5.3.0: 49/49 tests passed before and after, with the worktree verified. This run used a recipe-driven harness