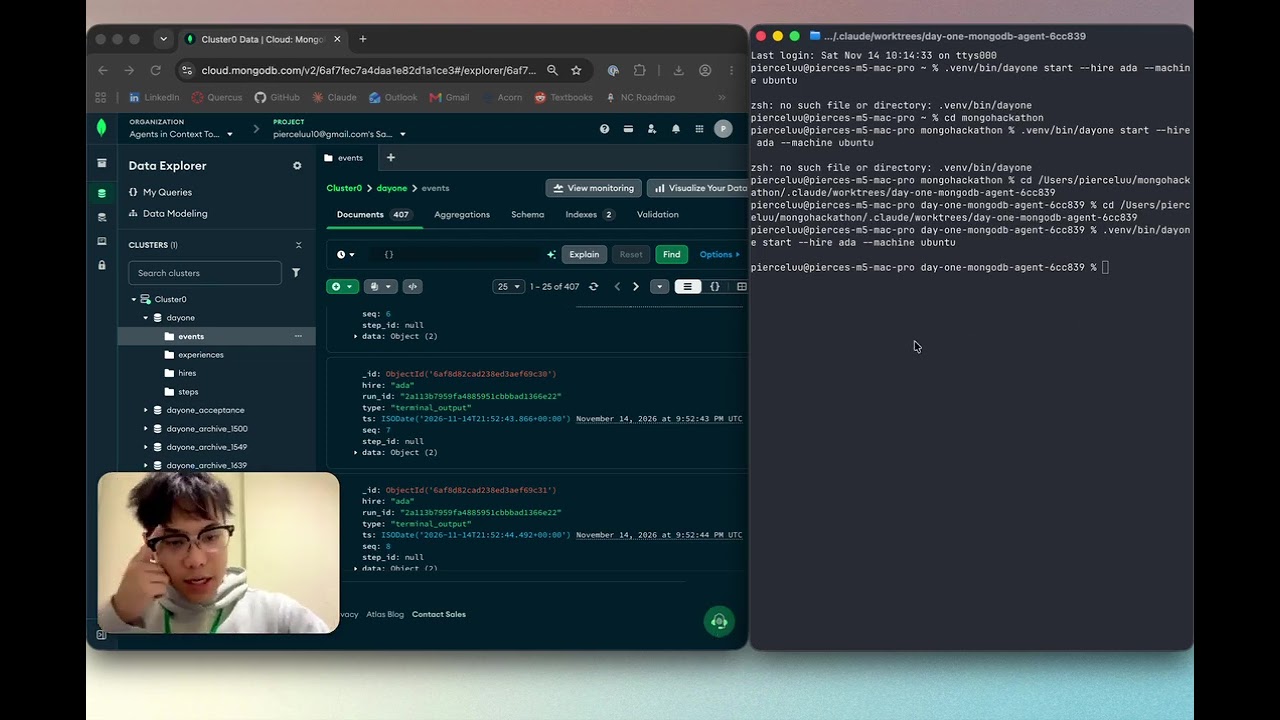
Our project lets an AI agent act on your money today. About nine million Canadians already share their banking credentials with third parties. Banks are now finding unauthorized AI agents inside customer accounts, and JPMorgan's CEO warned in October that banks can't let "just any outside agent" in. Institutions are stuck choosing between blocking agents, which gives up real automation like KYC reviews that cost thousands of dollars and take months, and allowing them on shared passwords, which means risk they can't monitor or attribute. Agent Warrant Protocol replaces the password with a warrant: bounded, time-limited, revocable terms that the customer approves with Touch ID. You describe what the agent may do in plain English, such as "$500 at a time, $1,000 max, NVIDIA only." It compiles into canonical terms with a clear worst-case line, and your passkey signs the hash of those exact terms, so changing a single field breaks the signature. Before the agent does anything, a deterministic gate with no LLM in the decision checks the action against the signed terms. It spends the budget in one atomic MongoDB operation, so 20 simultaneous $50 purchases against the $500 left give exactly 10 allowed and 10 denied. Allowed actions reach the brokerage with a signed receipt. The brokerage checks the gate's signature, the customer's own passkey signature and the terms for itself, instead of trusting the agent. Revoke the warrant, and the very next action fails. The same warrant governs data, not just money. When an agent tries to send customer information out, sensitive fields such as Social Insurance Numbers and account numbers are removed first. MongoDB Atlas Vector Search, with automatic embedding, then matches the outgoing payload against plain-English policies like "Require Touch ID before any account statement leaves our network." When a policy matches, release waits for a fresh Touch ID, signed over the hash of exactly what will be sent. Every decision is written to a hash-chained, gate-signed ledger in MongoDB Atlas before anything executes. That includes every blocked attempt. A reviewer can re-verify the customer's original signature at any time, and if someone edits a single record in the database, verification fails at that exact event. MongoDB carries the trust model throughout: transactions for atomic budgets, schema validation so a budget can never go negative, a compare-and-set ledger head that prevents forks, Vector Search for policies written in plain English, and change streams for the live audit view. Standards such as AP2 define signed payment mandates. AWP is the runnable layer around them that enforces, revokes and audits, for payments and beyond.
Team