Veil Privacy
Built at Meta Global AI Developer Hackathon · Oct 26, 2026 · Remote
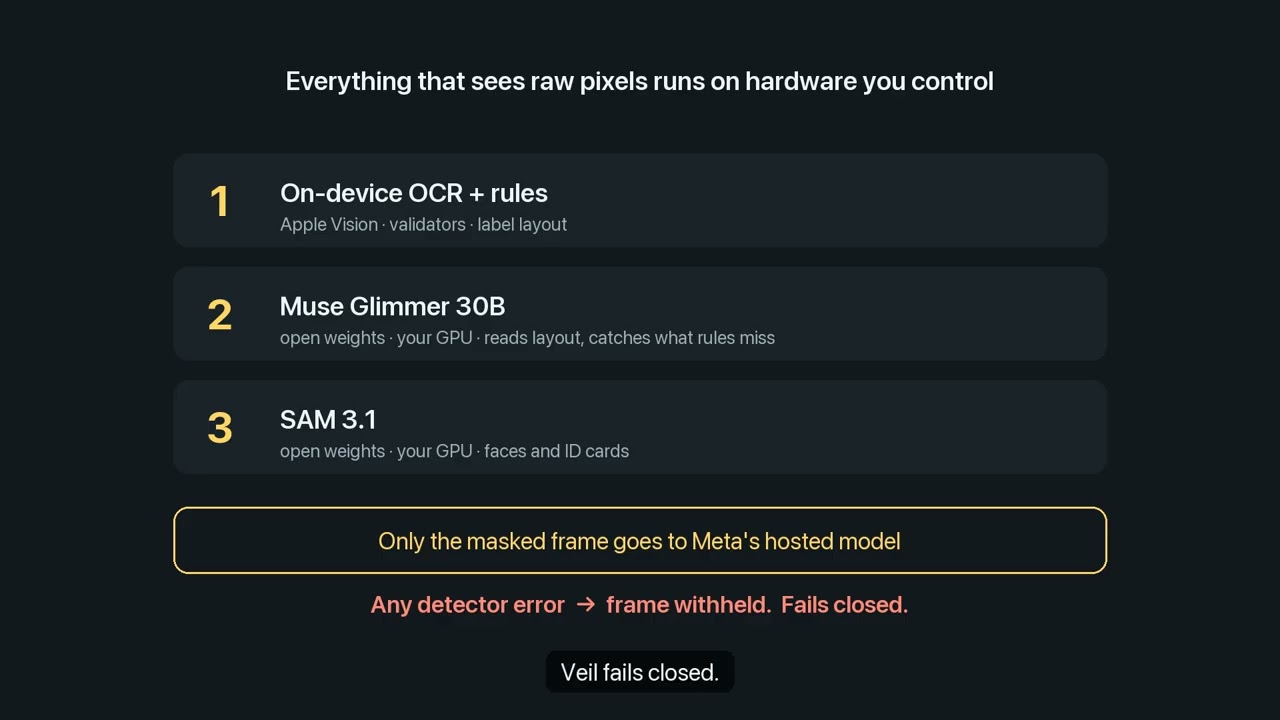
Veil is a privacy firewall for computer-use agents. These agents work by sending screenshots to a cloud model, so every patient name, member ID, date of birth and insurance card on screen leaves the machine. That is why healthcare, insurance and finance can’t use them. Veil is a drop-in proxy: change one line, the agent’s base_url. Before each screenshot leaves, on-device OCR plus Meta’s open-weight Muse Glimmer and SAM 3.1, running on GPUs I control, find personal data and cover it. Real values become tokens like NAME_1, so the agent can still do the job: it types {{NAME_1}} and Veil fills in the real name locally. Every value remembers where it came from, and a policy file decides where it may be written, so a prompt injection that fools the model still can’t send member data out. Sending, paying, or changing contact details waits for a human. Every step goes into a hash-chained audit log. It fails closed: if any check fails, the frame isn’t sent. Results on synthetic data: 0 of 170 sensitive values leaked on a held-out medical records app built after the rules were frozen (a typical regex redactor leaked 64%). A planted “workflow step” injection fooled the unprotected agent into sending member data in 4 of 8 runs; through Veil, 0 of 15. Task success matched the unprotected agent (6 of 6 vs 6 of 6), with about 2 seconds added per step at the median. Veil also runs as an MCP server.