Heist
Built at Meta Global AI Developer Hackathon · Oct 26, 2026 · Remote
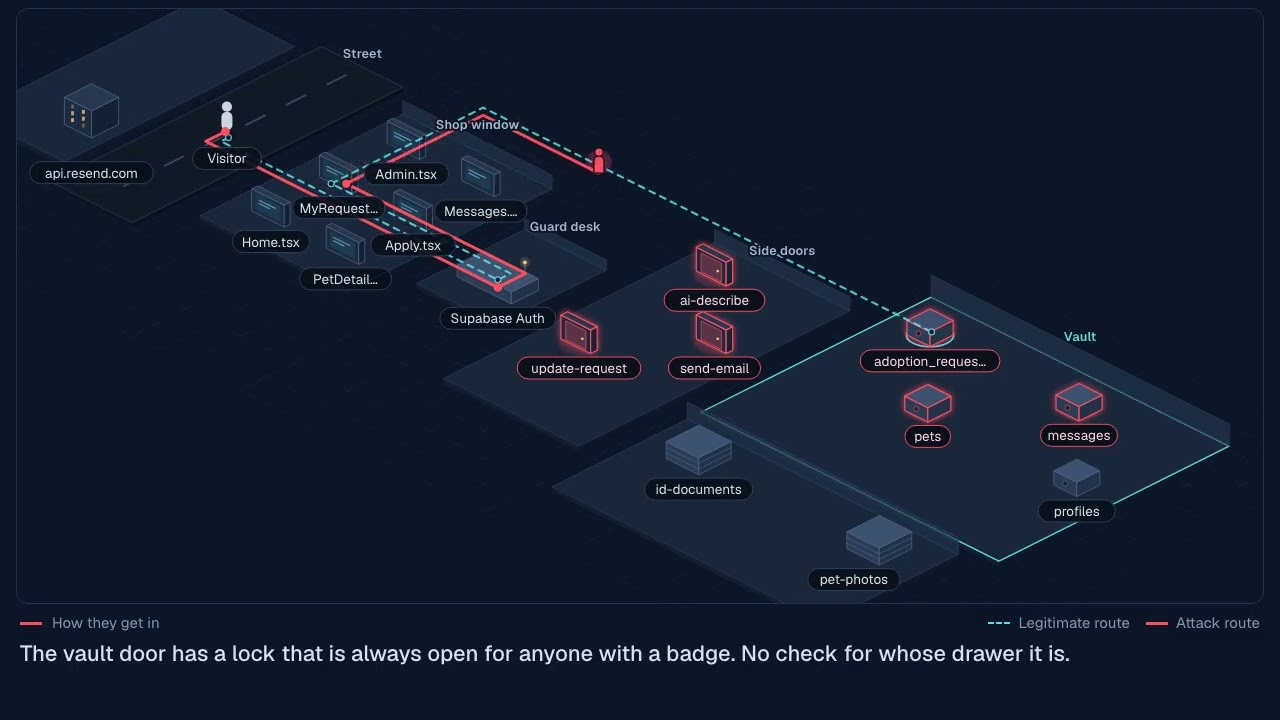
Heist: see how your vibe-coded app gets robbed, before someone else does. Live: https://heist-sepia.vercel.app Paste a public GitHub repo of a Lovable, Bolt or Next.js + Supabase app. Heist maps the app as an isometric city (street, shop window for browser code, guard desk for auth, side doors for edge functions, vault for tables, warehouse for storage) and replays the attack step by step, with Story, Why and Code tabs for non-coders and developers alike. Deterministic checks (Gitleaks, Semgrep and migration SQL parsing) find seven common mistakes: leaked keys, the Supabase admin key in browser code, open tables, open buckets, unauthenticated functions, missing owner checks, and paid APIs anyone can trigger. Every model answer is validated against the real files and lines. For database leaks Heist proves it: it applies the repo's migrations to a throwaway Postgres, seeds fake users (Test Alice and Test Bob), and reads the rows back as someone who should not see them. It never sends a request to the live app. Each finding ends with a code diff and a plain-language fix prompt to paste back into Lovable or Cursor, plus a "locks held" badge and an MP4/GIF export of the replay. On 50 public Lovable and Bolt apps, 46% had a confirmed critical issue and 72% at least one confirmed issue. Demo app: https://github.com/Bsahoo99/pawhaven (fixed: https://github.com/Bsahoo99/pawhaven-fixed). Replay: https://heist-sepia.vercel.app/a/zUgZGi3hZnDK