CodeGuard AI
Built at Meta Global AI Developer Hackathon · Oct 26, 2026 · Remote
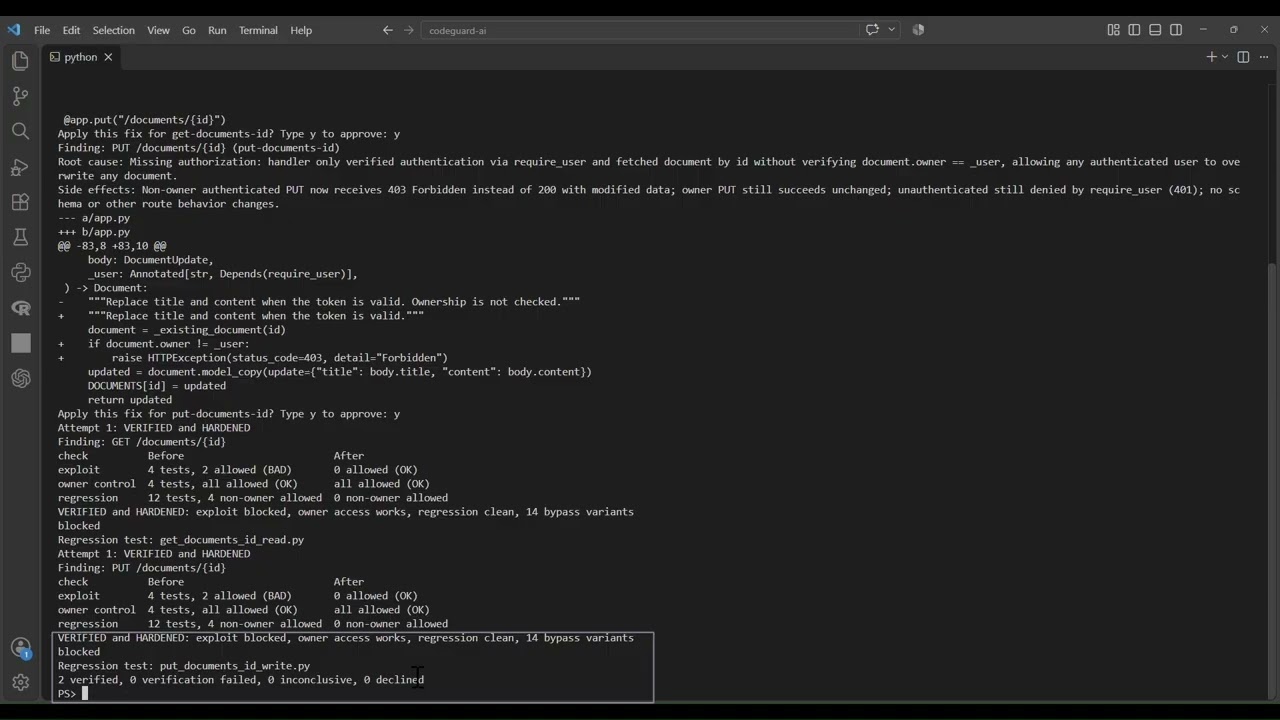
CodeGuard AI finds, proves, fixes, verifies, and regression-tests Broken Object Level Authorization (BOLA, OWASP API1) bugs in FastAPI apps. BOLA is the bug where one user changes an ID in a request and reads or changes another user's record. Ordinary tests usually call a route as its owner, so they rarely show what a different user can do. How it works. A scan reads the app's source with Python's ast module (the target is never imported or run during analysis), builds an authorization matrix, and asks a model to propose security tests through a read-only tool loop (list_routes, read_handler, get_matrix, submit_plan). The plan must match a strict schema and is validated against the known routes, users, and resources before anything is sent. Tests run only against the app running locally (localhost allowlist). A finding is Confirmed only when deterministic code sees a non-owner get access and the owner's own control request succeed. Timeouts, 5xx responses, and state-tainted results are Inconclusive, never evidence. Fix and verify. For each confirmed finding a model proposes a structured text edit. The patch is applied only to a temporary copy, and only after the developer types y. It counts as verified only if the exploit is blocked, the owner still has access, the regression set is clean, and 14 bypass variants fail. A failed fix is repaired up to twice. Each verified fix is exported as a regression test, and a one-page static HTML report ties the finding, evidence, diff, and verification together. Results (small local benchmarks, all measured in the repo): on 8 benchmark apps (7 vulnerable routes, 3 runs each), Muse Spark 1.3 and Muse Spark Open each confirmed 21 of 21 vulnerable-route runs with 0 false positives, and so did a run with no model at all. So detection is deterministic, and the models' measured value is writing and repairing patches: 20 of 20 fixes verified on the first attempt for each model. On 10 apps written by Muse Spark 1.3, CodeGuard confirmed no bugs, and the report lists what it could not judge (14 collection routes, 2 apps that did not start). None of the 8 benchmark apps is held out. Limits are in the README: localhost fixtures only, collection routes are not judged, one level of Depends() is followed, BFLA and BOPLA are out of scope, and it does not replace a security review. Built solo, Oct 27 to Nov 2, 2026. Code, reports, and every number: github.com/Keerthi156/codeguard-ai