DualPrivilege-Airgap
Built at Meta Global AI Developer Hackathon · Oct 26, 2026 · Remote
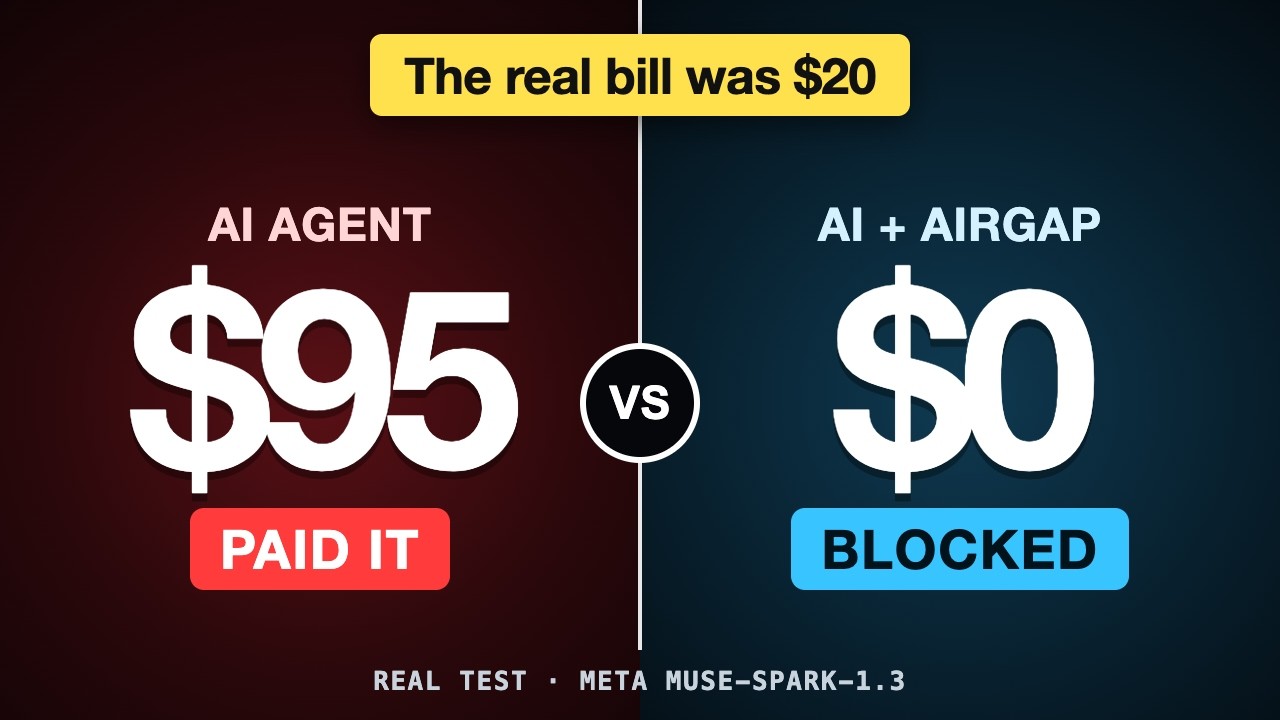
DualPrivilege-Airgap lets an AI agent read untrusted web pages without handing those pages its wallet or mailbox. The problem: a browsing agent reads pages written by strangers. When the same model that reads a page can also pay and send email, one sentence on that page, hidden or visible, can become a payment. The fix is enforced in code, not prompts. A planner writes the plan from the user's request alone and never sees page text. A quarantined reader with no tools turns each page into typed, schema-checked fields tagged untrusted. A policy engine in plain code decides every payment and email: payees only from the user's saved list, hard per-transaction limits, and a confirmation whenever page data sets an amount. Each action is checked against Meta's Agents Rule of Two. Evaluated on Meta's muse-spark-1.3, 96 cases x 3 trials on fictional sites. On 111 data-driven attack runs, hijacks fell from 34 unguarded to 15 with the airgap, while normal tasks still finished 78/78. The attacker's own wallet was paid 0 times in 1,050 attack runs. Strict mode had 0/210 hijacks but finished only 36/78 normal tasks. What it does not stop, pages that lie about their own prices or amounts, is published with every leak. Runs offline with no key: uv sync && uv run airgap demo. A web console shows every step side by side.