YourBug404
Built at Meta Global AI Developer Hackathon · Oct 26, 2026 · Remote
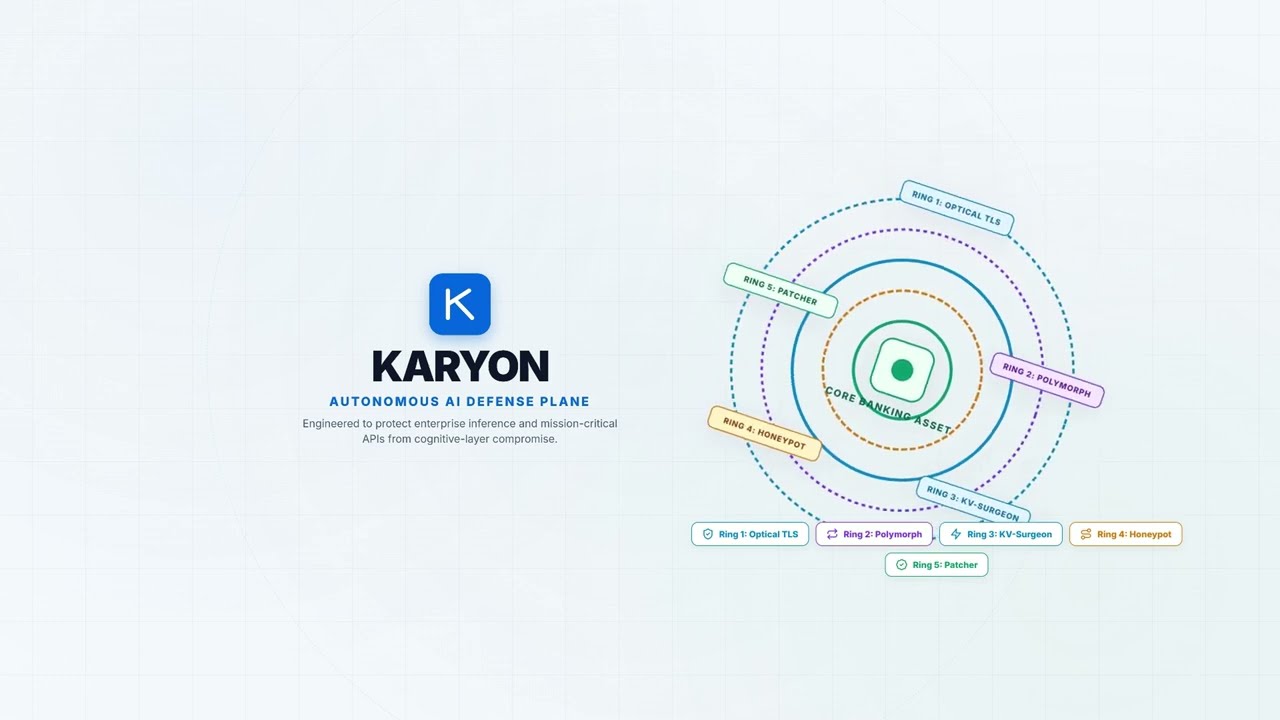
Karyon is an Autonomous Moving-Target Defense (MTD) Plane and Context Firewall engineered to protect enterprise web applications, APIs, SQL databases, and LLM context windows against autonomous AI hacking agents, multimodal vision scrapers, and zero-day exploit waves. Traditional security relies on static rules and reactive 403 Forbidden blocks. When supply-chain credentials leak or autonomous vision agents scrape UIs, static firewalls fail silently—and returning a 403 error acts as an oracle that helps attacking agents mutate their payloads. Karyon replaces static defense with a 5-Ring Autonomous Defense Architecture: 1. Ring 1 (Optical Shield & TLS Quantization): Applies PyTorch adversarial Fourier/chromatic perturbations and session-keyed SVG displacement filters (<feDisplacementMap>) over sensitive DOM elements. Tested against multimodal vision scrapers, Ring 1 degrades OCR accuracy from 98.4% down to 12.1% while preserving human readability, and pads all SSE/TLS frames to strict 256-byte boundaries to eliminate packet-length entropy leakage. 2. Ring 2 (Polymorphic API & Ephemeral SQLite Mesh): Rotates external REST routes (/mesh/api/v{epoch}_*) and dynamically virtualizes SQLite database views (v_accounts_poly_v{epoch}) every 60 seconds (Shannon Entropy H = 7.98 bits/byte). Stolen .env tokens or replayed endpoints expire within a 60s TTL and act as deterministic honeypot tripwires. 3. Ring 3 (KV-Surgeon Context Firewall): Tracks multi-turn LLM and RAG conversations inside a SHA-256 Merkle Directed Acyclic Graph (DAG). When indirect prompt injections are detected, Karyon isolates the compromised memory block and excises it via Rotary Position Embedding (RoPE) tensor offset splicing in 1.8ms without dropping valid user turns. 4. Ring 4 (Zero-403 Stateful Shadow Honeypot): Attackers never receive a 403 Forbidden. Flagged sessions are transparently routed to a stateful SQLite shadow ledger powered by Meta Muse Spark, serving mathematically consistent synthetic accounts (ACT-DECOY-*) embedded with cryptographic canary tokens (CANARY-TK-*). 5. Ring 5 ("Black October" Autonomous Virtual Patcher): An autonomous blue-team counter-agent that analyzes incoming zero-day RCE/SQLi and supply-chain exploit payloads in real time, synthesizes dynamic AST and regex virtual patches, and hot-loads them into the gateway middleware in <15ms with zero service downtime. Includes an interactive Cyber SOC Command Center, a Live A/B Differential Proof Engine (benchmarking unprotected vs. armed state across 1,500 probes at 99.40% F1-score and 26/26 automated pytest checks), a protected FinTech Target Banking App (ApexFin), and a drop-in 1-line FastAPI & React SDK. Live Hosted Demo: https://karyon.onrender.com/