Dirty Deeds
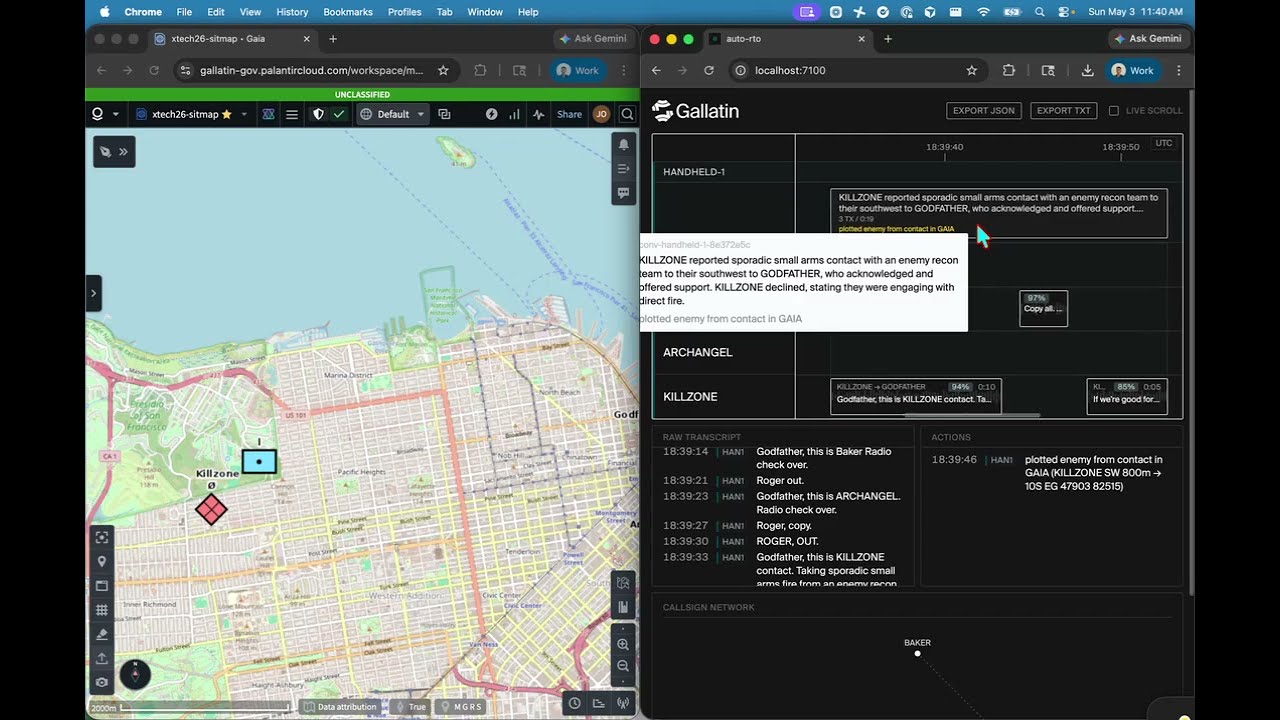
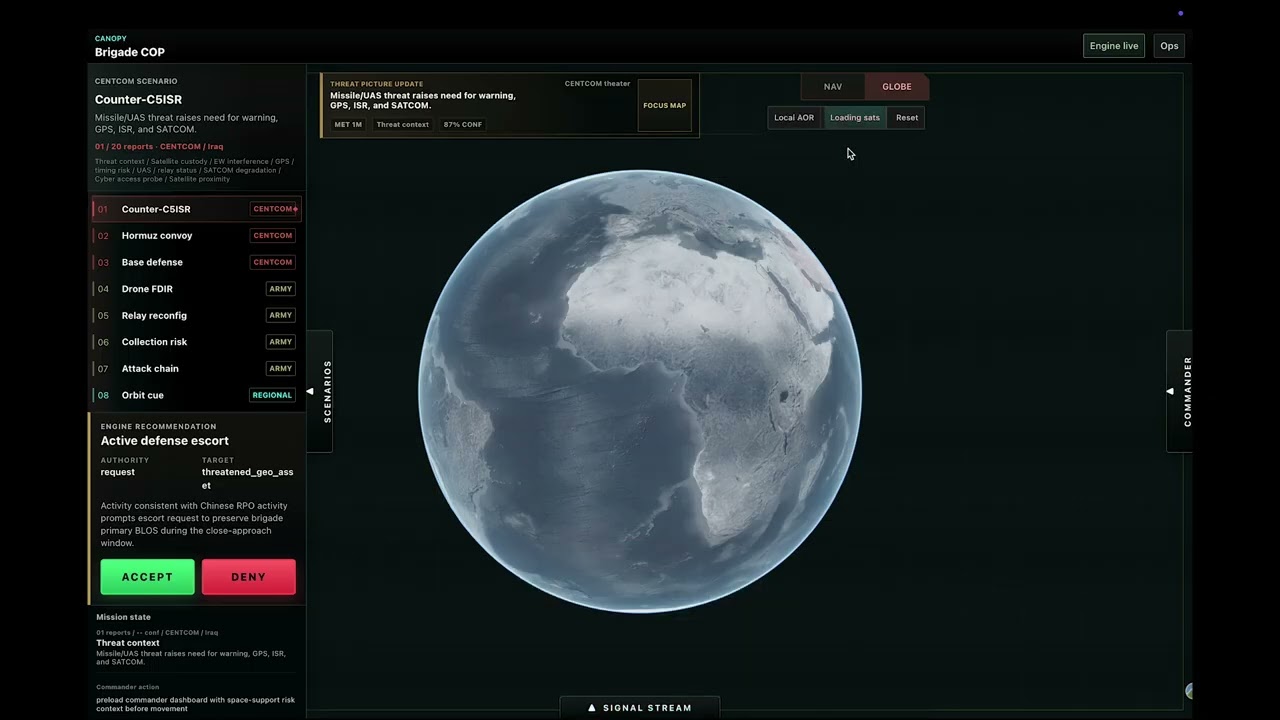
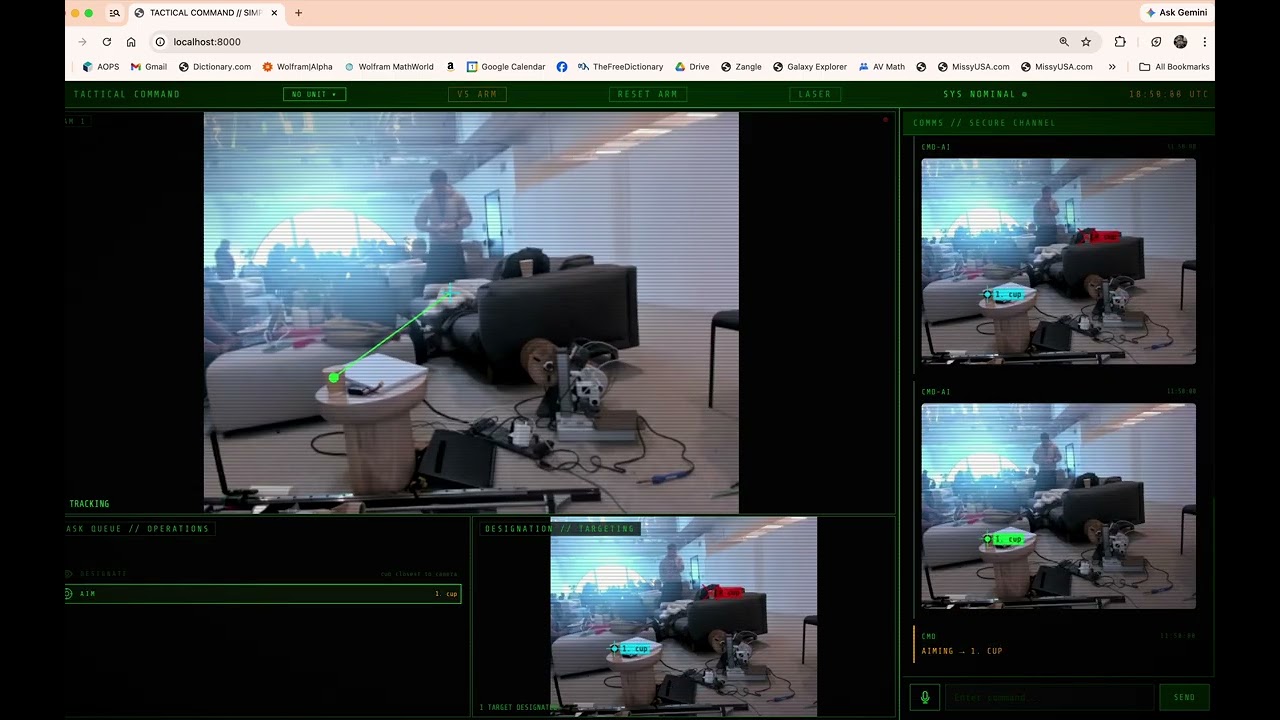
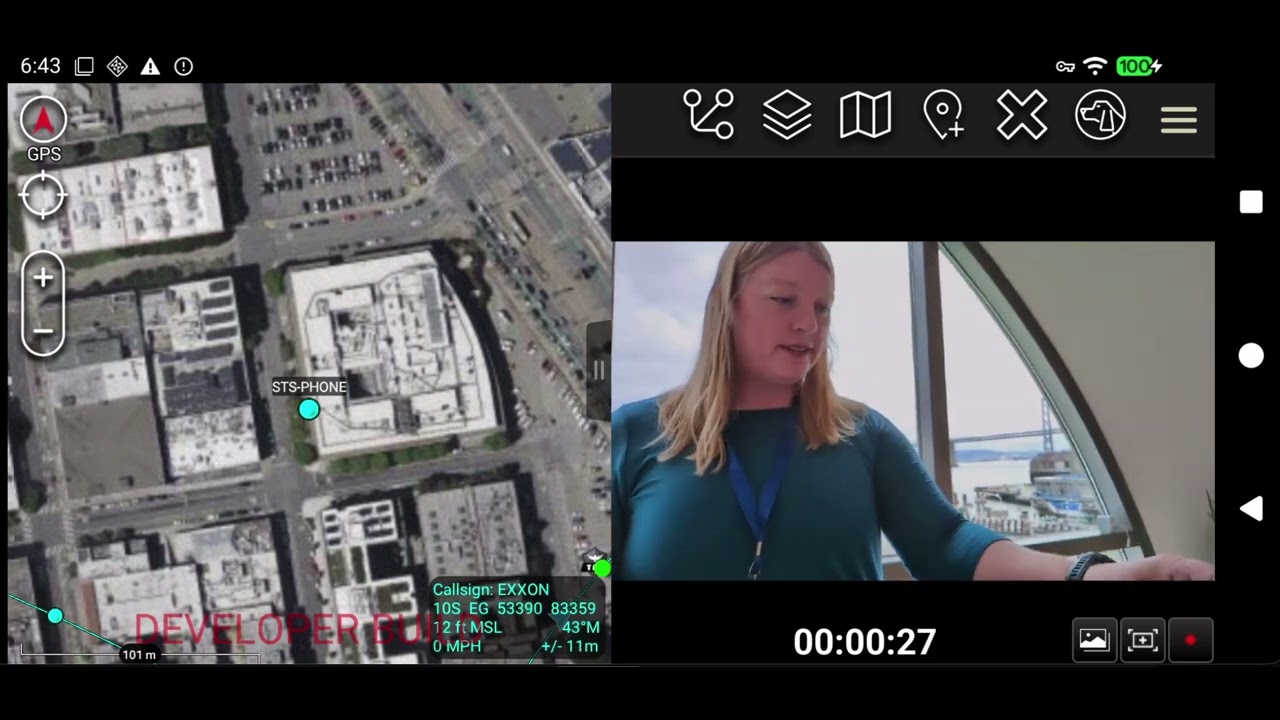
National Security Hackathon (by Army xTech)We had to update the link from youtube as it would not generate the link at https://studio.youtube.com/channel/UCiYqw2-65DuCkB0WMsu2nSQ -> USE VIMEO https://vimeo.com/manage/videos/1188853828 Project Dirty Deeds: We are running inside of Palantir for this demonstration. We are not able to take the code outside of the platform. Operator data is never exposed. Nothing is transmitted in a human readable format. You need the corresponding key to un-encrypt any and all data flowing across the chain. Overview of Solution - We built a solution for military and intel use that we believe cross cuts many of the problem statements outlined for this hack. A "Non-transferable, hardware-bound, software-attested identity.” We take cryptography and make it more lightweight. We implemented a SBNFT structure for the attestation layer, implementing Post Quantum Cryptography in an Open Attestation Protocol within a 23 byte message for Digital Defense. We believe, what we bring, also solves problems that exist within Mission Command and Control by improving decision making that accelerates the kill chain while painting a unified, explainable and forensically viable operational picture. Real time attestation - Please refer to video on the Palantir platform. On Chain recording - As you can see, we are attesting on chain in real-time. The table above gives examples of situations where attestations should be made. Post Mortem analysis - There are several reasons we believe this is helpful to our intel and warfighter communities. Often, a soldier is asked to recall details - hardware lapses, signal failures, and so on. Now, the AAR can include these details in a cryptographic sense. How, when or from whom did the delay originate. Is this situational, or systemic? Having this information to review in the AAR, along with every other decision and data point used in the battle space, would take the burden off of the operator and give a new level of actionable data that would inevitably lead to quicker identification of problems and deployment of solutions. We’re going for fast and accurate, explainable and responsible. Conclusion: We believe we can apply this model to everything from tanks to comms links. The entire problematic history of an attested piece of hardware available on a tablet that is authorized and attested. Sensor or radio communications attested as they arrive to a fellow attested device. No man in the middle attack. The operator's SBNFT proves device + person + software. The attestation on the brief proves it was not modified. The chain of custody is cryptographic — not dependent on logs that can be deleted, or screenshots that can be faked.” One audit trail. No vendor silos. GPS Denied offline verification - no network required. Zero code changes.
Team

Placement
Participant